The ASD Cyber Threat Report 2024–25, in five charts
ASD’s ACSC responded to 1,253 cyber security incidents last financial year and took more than 84,700 cybercrime reports. Here are the five figures from that report an Australian business can act on, with every number printed underneath.
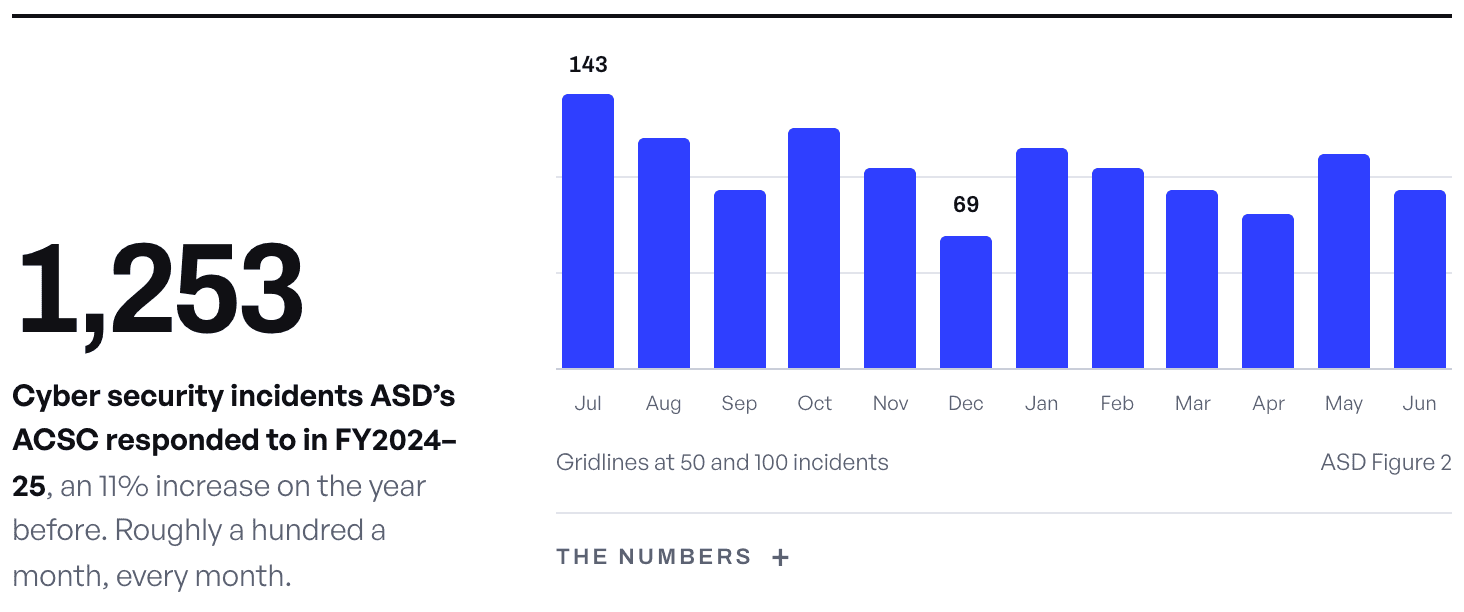
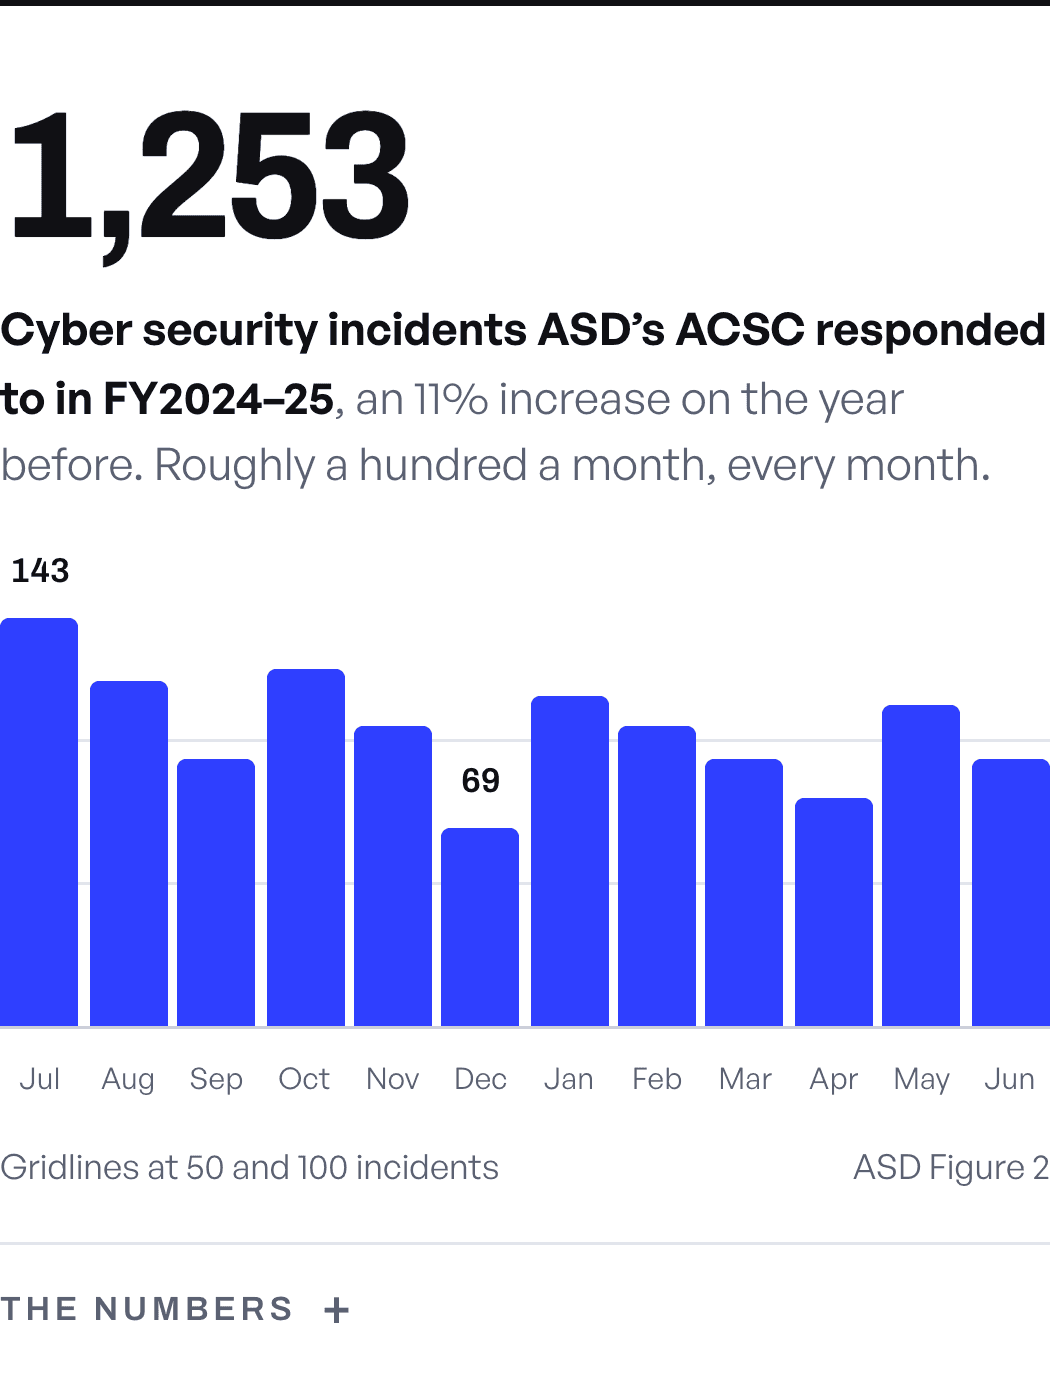
The numbers: Cyber security incidents ASD’s ACSC responded to, by month, FY2024–25
Month | Incidents |
|---|---|
July | 143 |
August | 120 |
September | 93 |
October | 125 |
November | 105 |
December | 69 |
January | 115 |
February | 105 |
March | 93 |
April | 80 |
May | 112 |
June | 93 |
Total | 1,253 |
How to read these numbers
ASD’s Annual Cyber Threat Report counts what Australians told ASD about. Three things follow from that, and they shape every chart on this page.
Reports are a floor, not a total. ASD says plainly that the vast majority of cybercrime goes unreported. Every count here is the visible part.
Technique percentages overlap. One incident can carry several MITRE ATT&CK techniques and several incident types, so the columns add to more than 100%.
Costs are self-reported. ASD flags the large-business figure itself: fewer large businesses reported this year, which leaves the average exposed to outliers. We have kept that caveat next to the chart rather than in a footnote.
Average self-reported cost of cybercrime, per report
ASD Figure 3. Small business has climbed for three straight years. Large business tripled in one.
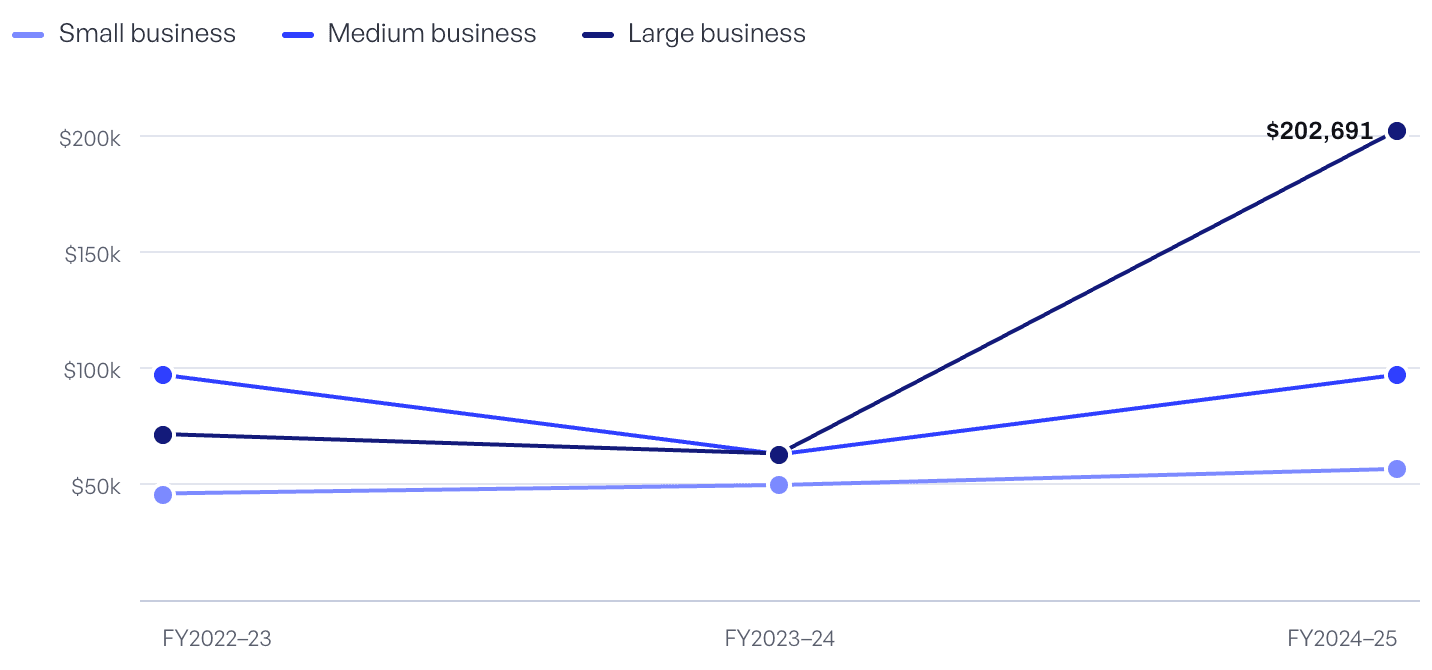
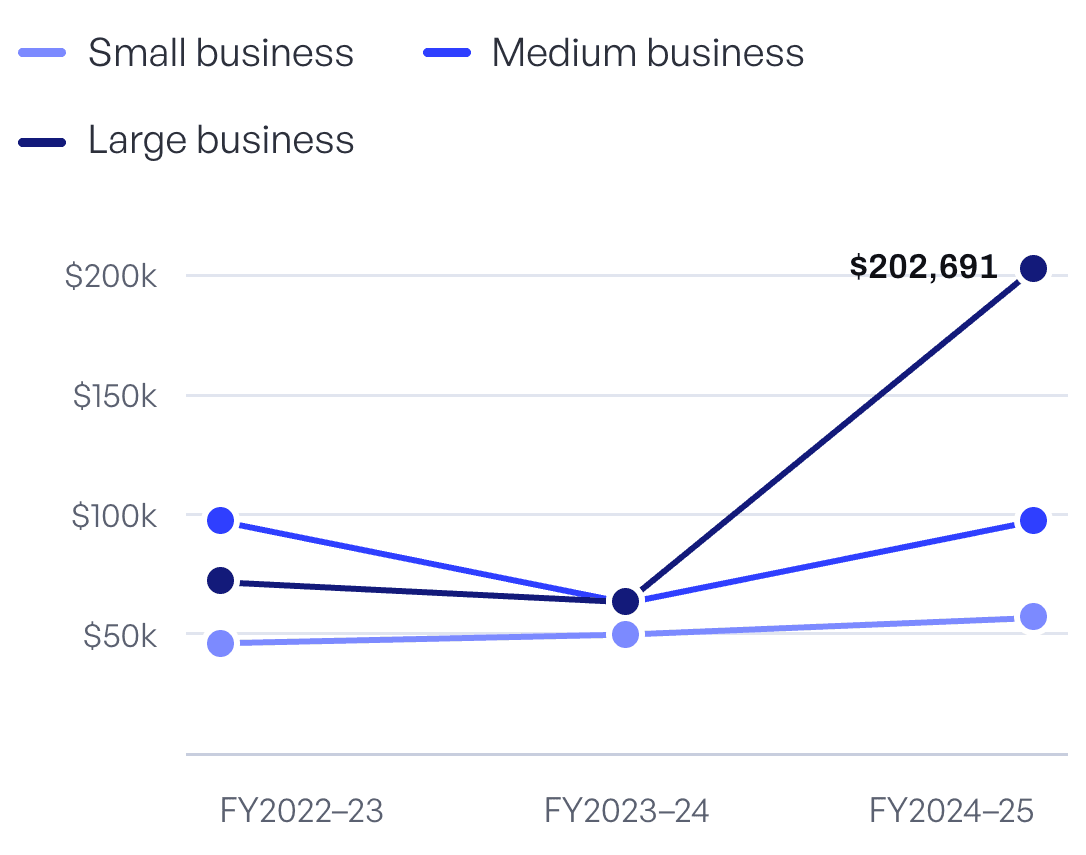
ASD’s caveat, in full: part of the large-business jump tracks a 138% rise in total BEC losses for large business, and part of it is arithmetic — large-business reports fell 22% year on year, and a thin denominator moves an average a long way. Large businesses file just over 12% of all business reports.
The numbers: Average self-reported cost of cybercrime per report, by business size
Business size | FY2022–23 | FY2023–24 | FY2024–25 |
|---|---|---|---|
Small | $45,965 | $49,615 | $56,571 |
Medium | $97,203 | $62,870 | $97,166 |
Large | $71,598 | $63,202 | $202,691 |
A third of business reports start in a mailbox
Business cybercrime reports. Email compromise with a financial loss, and email compromise without one, are the two biggest categories of business cybercrime report. Together they are 34% of the total.
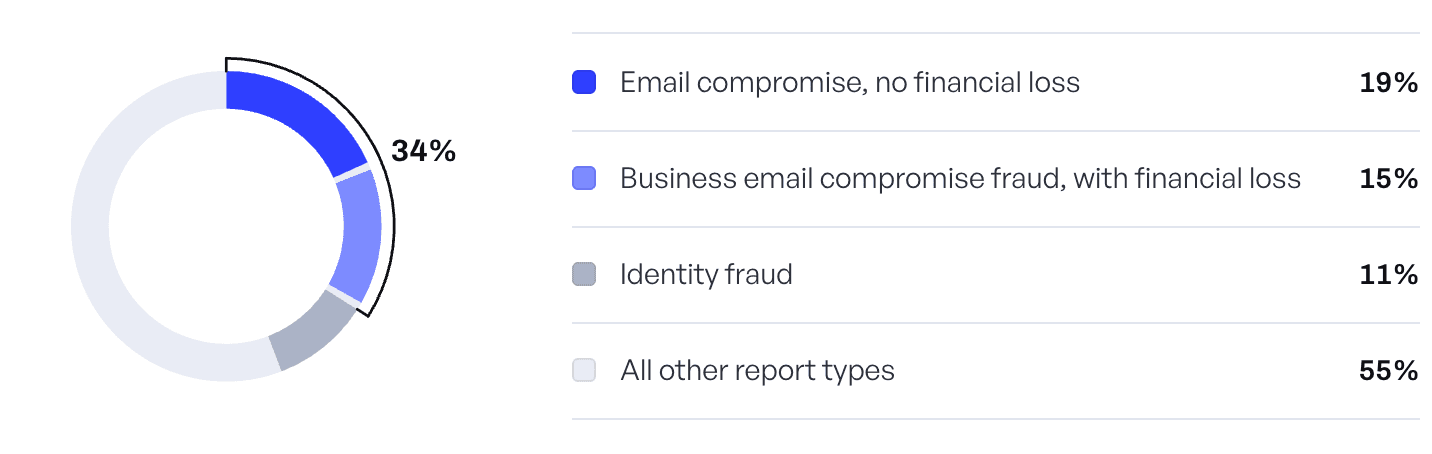
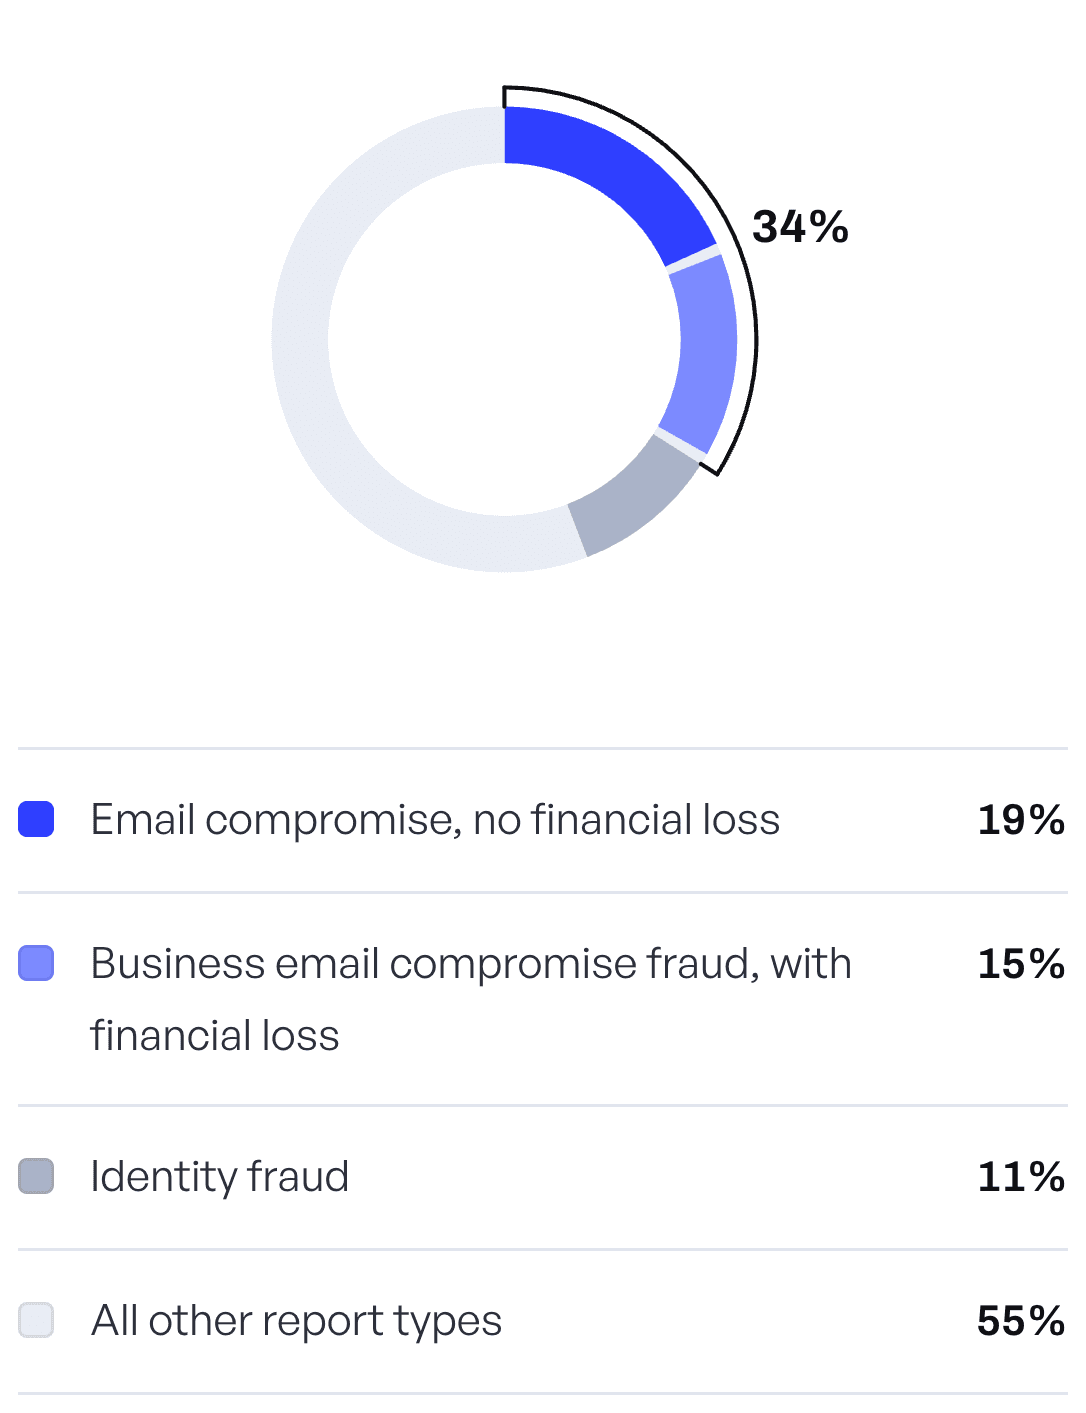
Shares of self-reported cybercrime reports from small, medium and large business. “All other report types” is the balance of the reporting categories, which ASD does not break out further in this figure.
The numbers: Top self-reported cybercrime types for Australian business, FY2024–25
Report type | Share of business reports |
|---|---|
Email compromise, no financial loss | 19% |
Business email compromise fraud, with financial loss | 15% |
Identity fraud | 11% |
All other report types | 55% |
For comparison, individuals report a different mix: identity fraud 30%, online shopping fraud 13%, online banking fraud 10%. The business list is dominated by the mailbox because that is where the money moves — an attacker who can read a thread about an invoice knows who pays whom, on what terms, and in what tone.
We wrote up how that plays out, and the controls that catch it, in business email compromise.
Top 10 reporting sectors, as a share of all incidents
ASD Figure 6. Government files 46% of everything ASD sees, because government has to report. The industry rows underneath are the market signal.
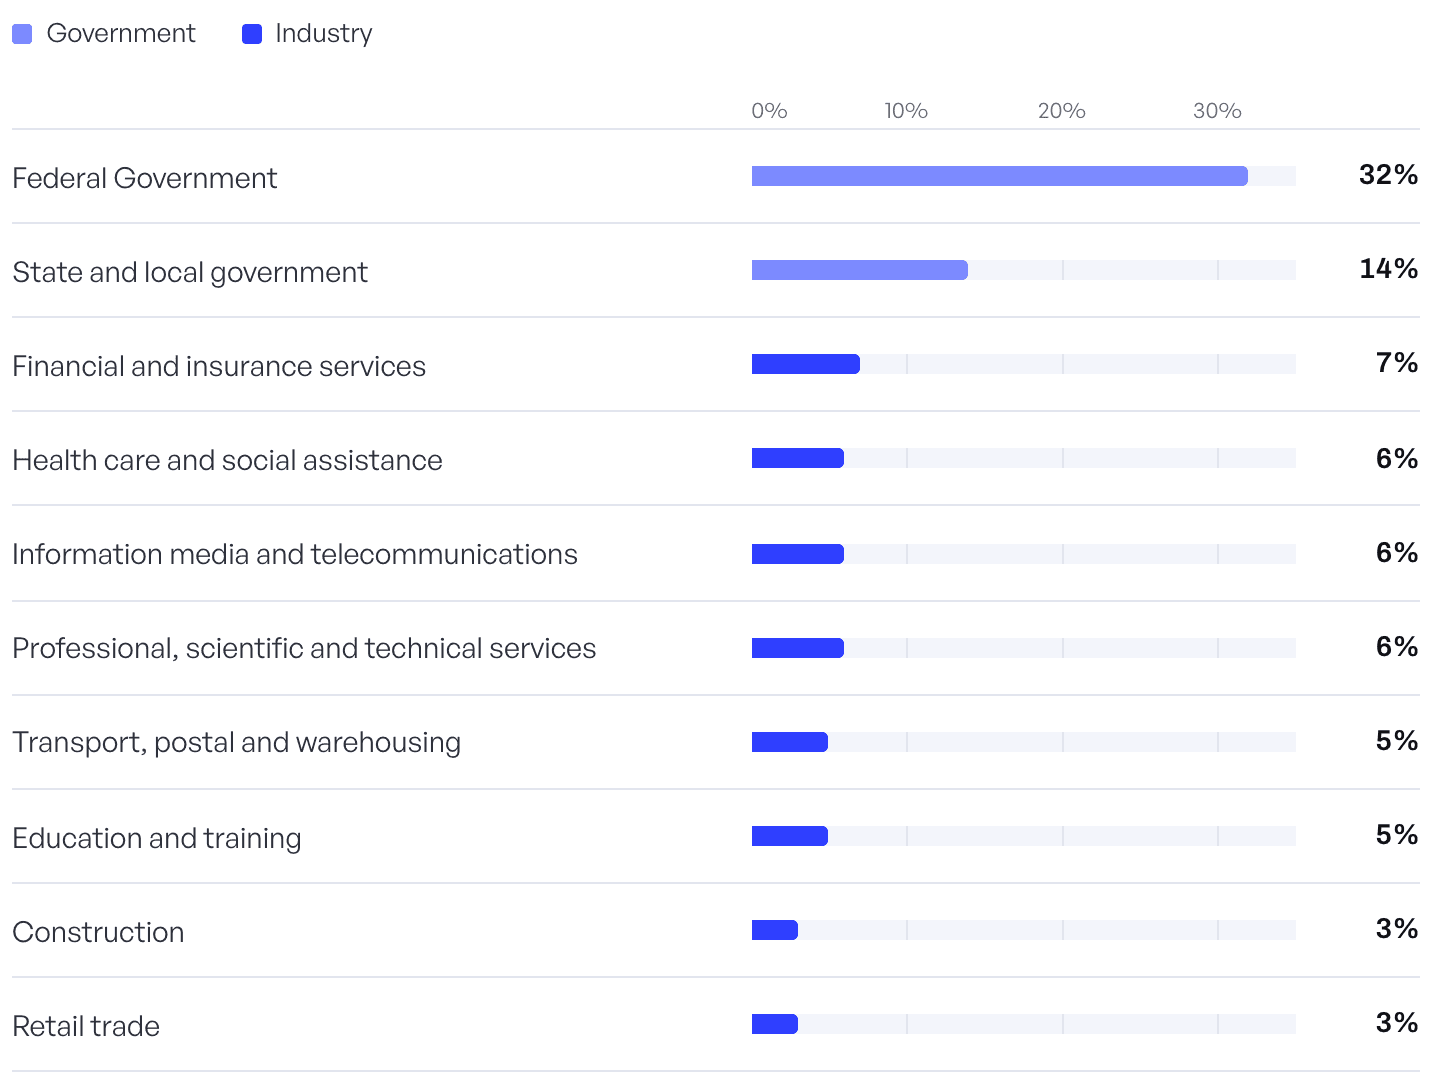
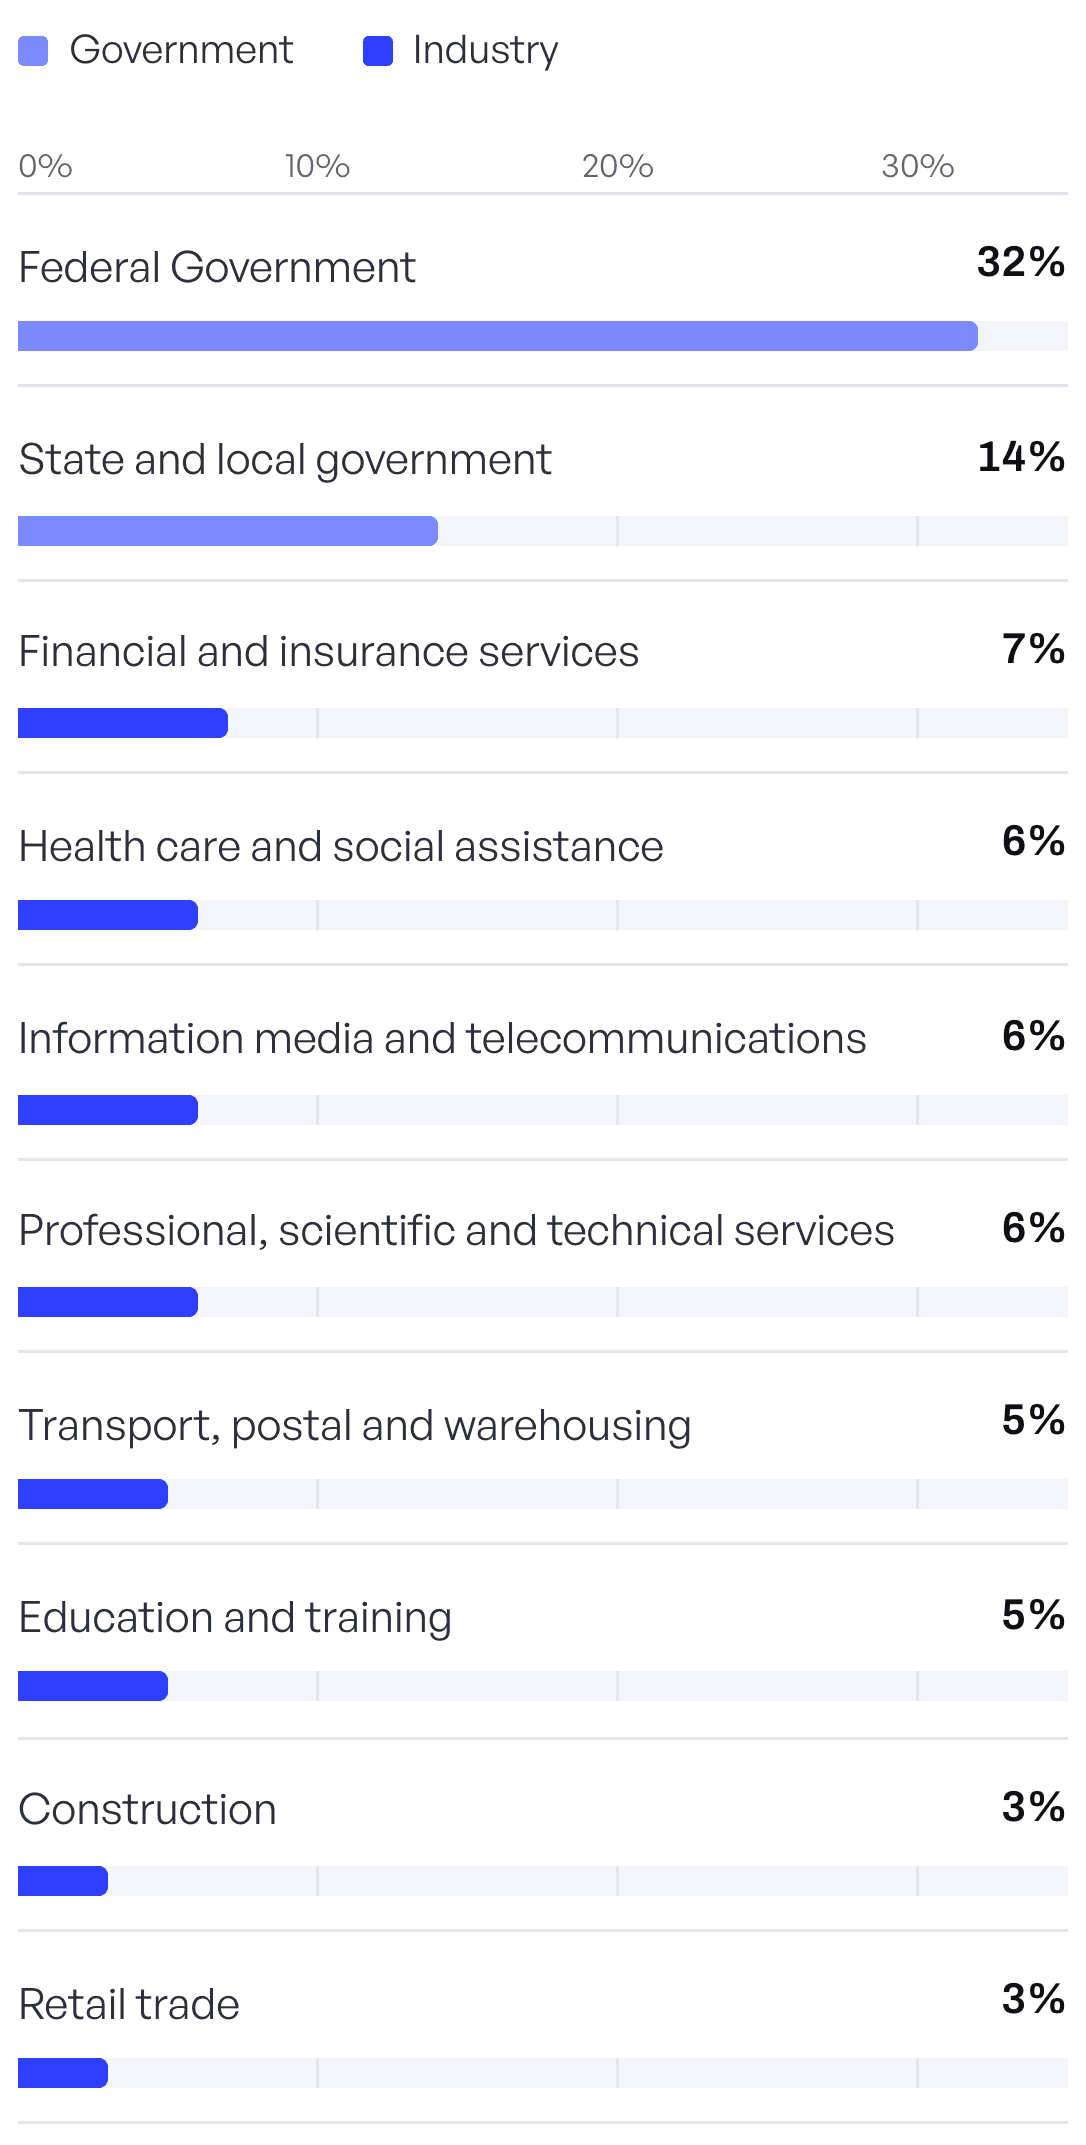
Financial and insurance services became the most frequently reporting non-government sector this year, lifted by DDoS activity against the sector. Federal Government reporting fell from 37% to 32%; state and local rose from 12% to 14%. Education and training left the top five.
The numbers: Top 10 reporting sectors, share of all incidents reported to ASD’s ACSC, FY2024–25
Sector | Share of incidents |
|---|---|
Federal Government | 32% |
State and local government | 14% |
Financial and insurance services | 7% |
Health care and social assistance | 6% |
Information media and telecommunications | 6% |
Professional, scientific and technical services | 6% |
Transport, postal and warehousing | 5% |
Education and training | 5% |
Construction | 3% |
Retail trade | 3% |
The same techniques, reported differently
ASD Figure 9. Rows are sorted by the gap between the two readings, so every technique government reports more often sits above every technique industry reports more often. The crossover is the finding: government reporting captures the approach, industry reporting captures the damage.
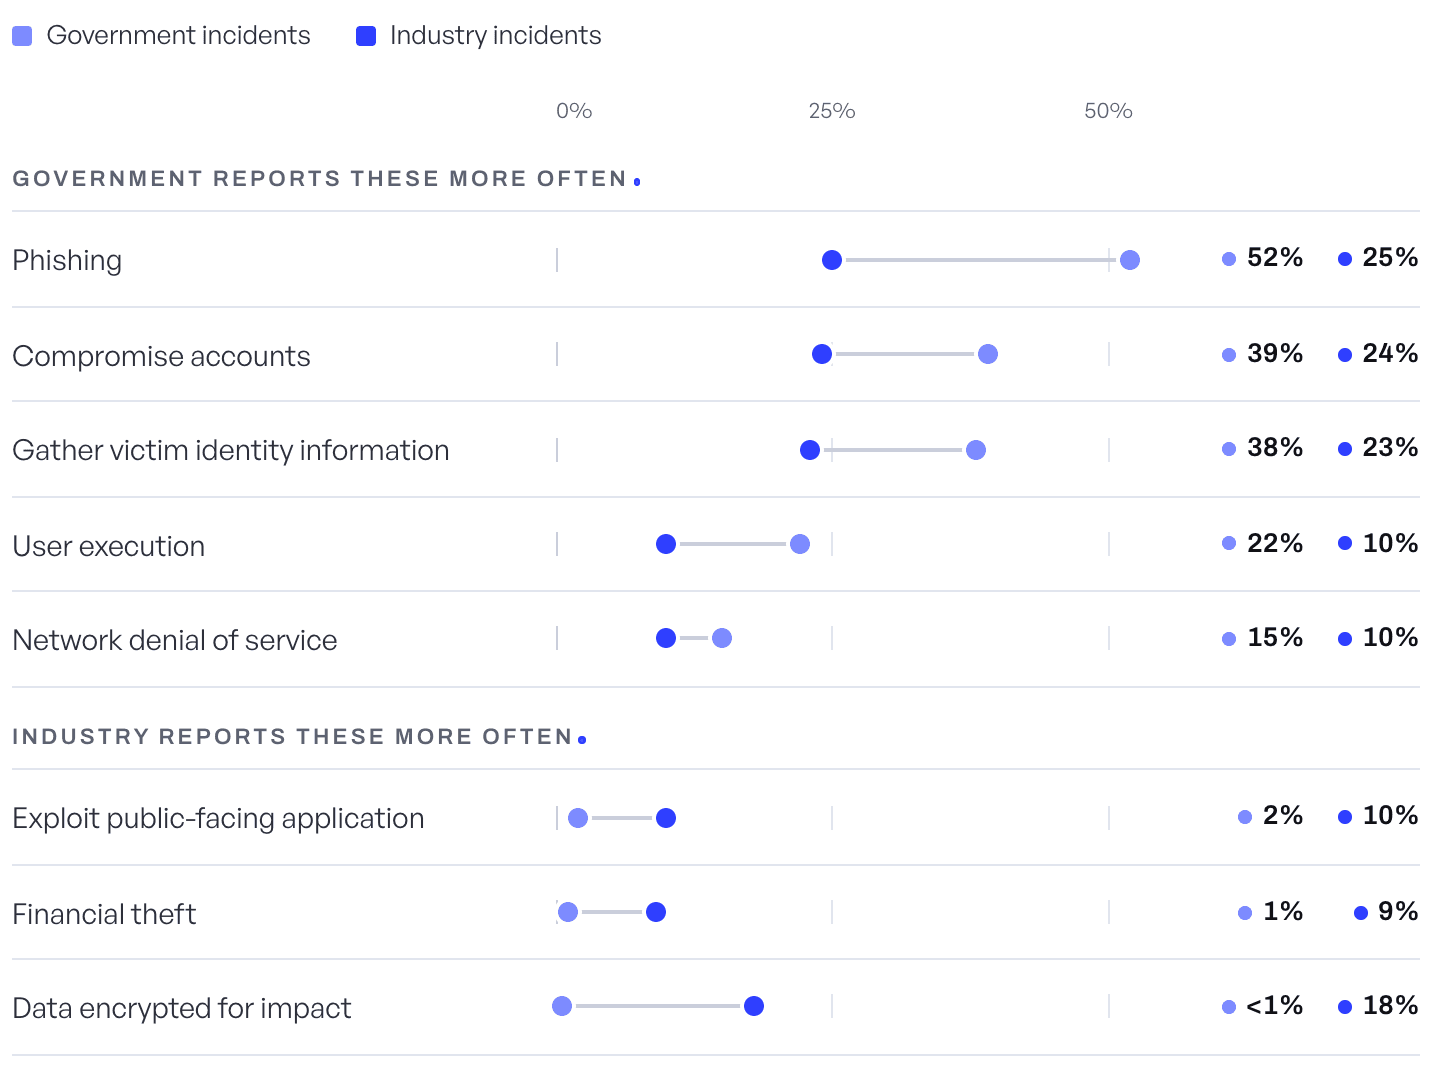
Eight techniques where ASD publishes both readings. Percentages describe the share of incidents in which the technique was identified, and one incident can carry several, so the columns add to more than 100%. Across everything ASD saw, phishing was recorded as an initial access technique in 38% of incidents.
The numbers: MITRE ATT&CK technique prevalence, government against industry reporting, FY2024–25
Technique | Government | Industry |
|---|---|---|
Phishing | 52% | 25% |
Compromise accounts | 39% | 24% |
Gather victim identity information | 38% | 23% |
User execution | 22% | 10% |
Network denial of service | 15% | 10% |
Exploit public-facing application | 2% | 10% |
Financial theft | 1% | 9% |
Data encrypted for impact | <1% | 18% |
Three techniques carry the whole industry column: encryption, edge exploitation and payment fraud. They correspond to three questions a business can answer this quarter. Can we restore from backup inside a working day? Do we know every service we expose to the internet, and is each one patched? Does a change of bank details require a call to a number we already held?
Critical infrastructure
Critical infrastructure made up 13% of all incidents, up 2 points on last year. The mix is different from the national picture: scanning or reconnaissance led to 41% of CI incidents, DoS and DDoS 31%, and phishing 20%. Denial of service showed up almost twice as often against CI entities as it did across all incidents, at 31% against 16%.
By division, CI incidents concentrated in financial and insurance services (32%), transport, postal and warehousing (26%), and information media and telecommunications (16%).
Healthcare is the sector to watch. Ransomware incidents against healthcare doubled year on year, and malicious actors succeeded in 95% of the health care and social assistance incidents ASD responded to, against roughly 52% across all sectors. We have written separately about what that means for Australian medical practices.
What we would do with this
Four numbers from this report govern where the money goes for a mid-sized Australian organisation.
34% of business reports involve email. Phishing-resistant MFA on every identity, a payment-change process that leaves the mailbox, and DMARC at enforcement. See cyber security and SPF, DKIM and DMARC.
18% of industry incidents involved data encrypted for impact. Offsite backups with a restore tested on a schedule, and the restore time written down. See backup and continuity.
10% of industry incidents began at a public-facing application. An inventory of everything you expose, patched on a clock. This is Essential Eight territory — see Essential Eight and ISM, and what ASD replacing it means for work already under way.
1,253 incidents, spread evenly across twelve months. Detection and response has to run when your office is closed. December was ASD’s quietest month at 69 incidents, and 69 is still more than two a day. See detection and response.
A technology assessment scores you against the Essential Eight, inventories what you expose, and tests a restore. You keep the written position whether or not you engage us.
Source for every figure on this page: ASD Annual Cyber Threat Report 2024–25 and its accompanying fact sheets for business and for critical infrastructure, published October 2025. Figures describe incidents and reports made to ASD’s ACSC.
Related reading
Type
Data
9 min read
Bryan Lam
Book an assessment
Find out where your organisation sits in these numbers
A technology assessment counts every asset, identity and licence, scores you against the Essential Eight, tests a restore and puts a costed sequence against what it finds. You keep the written position either way.